Explainers: Dependencies
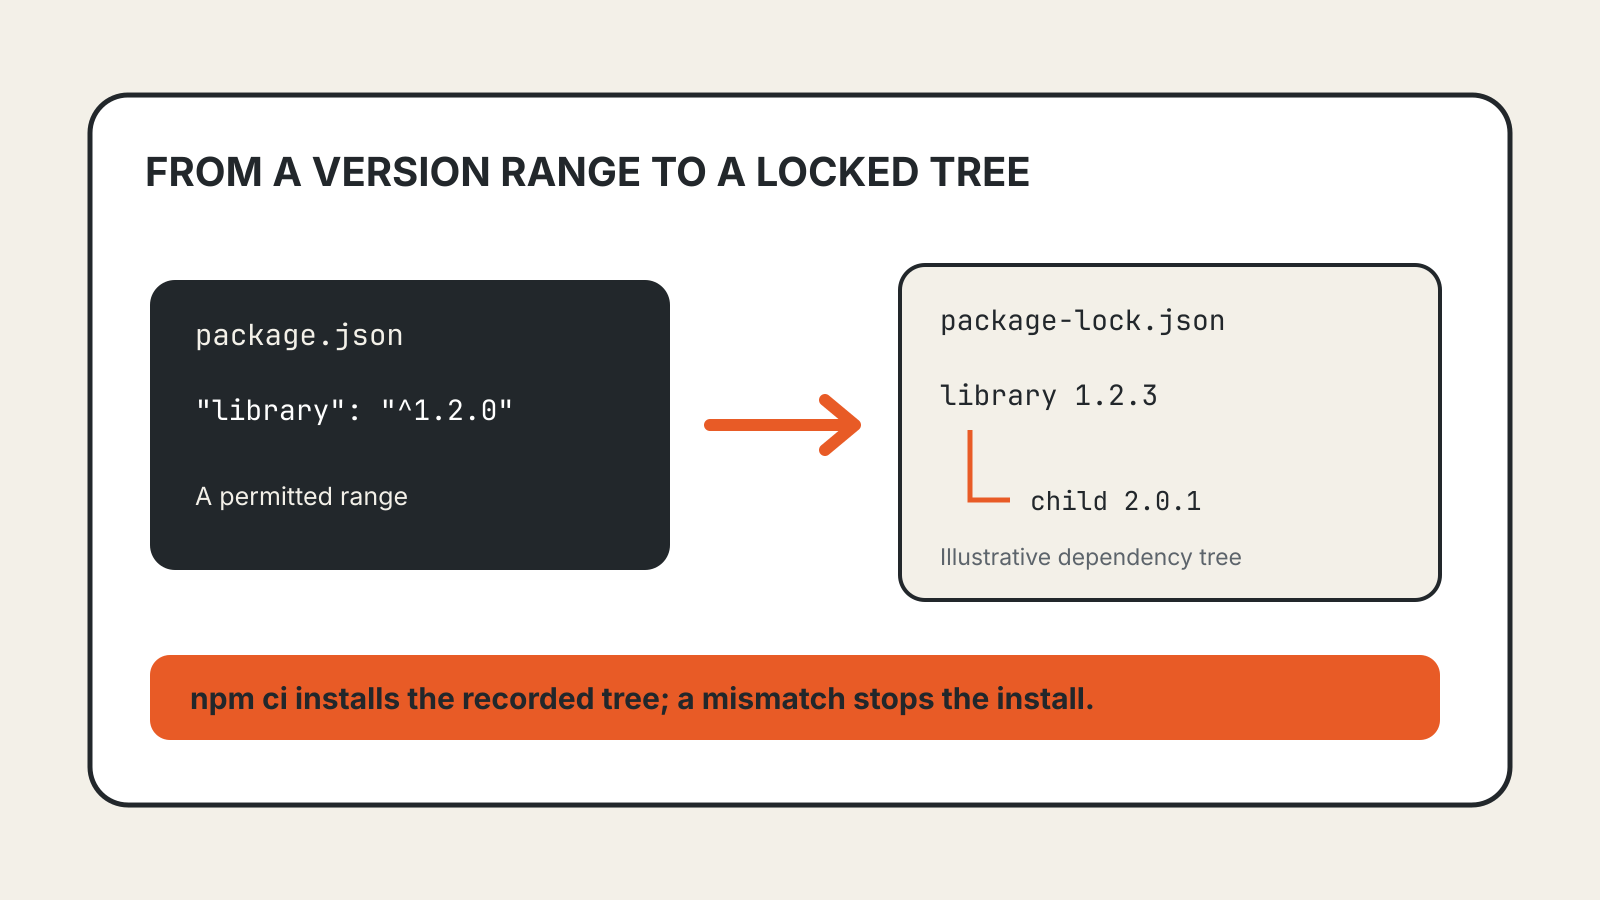
Lock File Explained: What Dependency Installs Preserve
How npm lock files record dependency versions, why npm ci rejects mismatches, and what a lock file cannot guarantee.
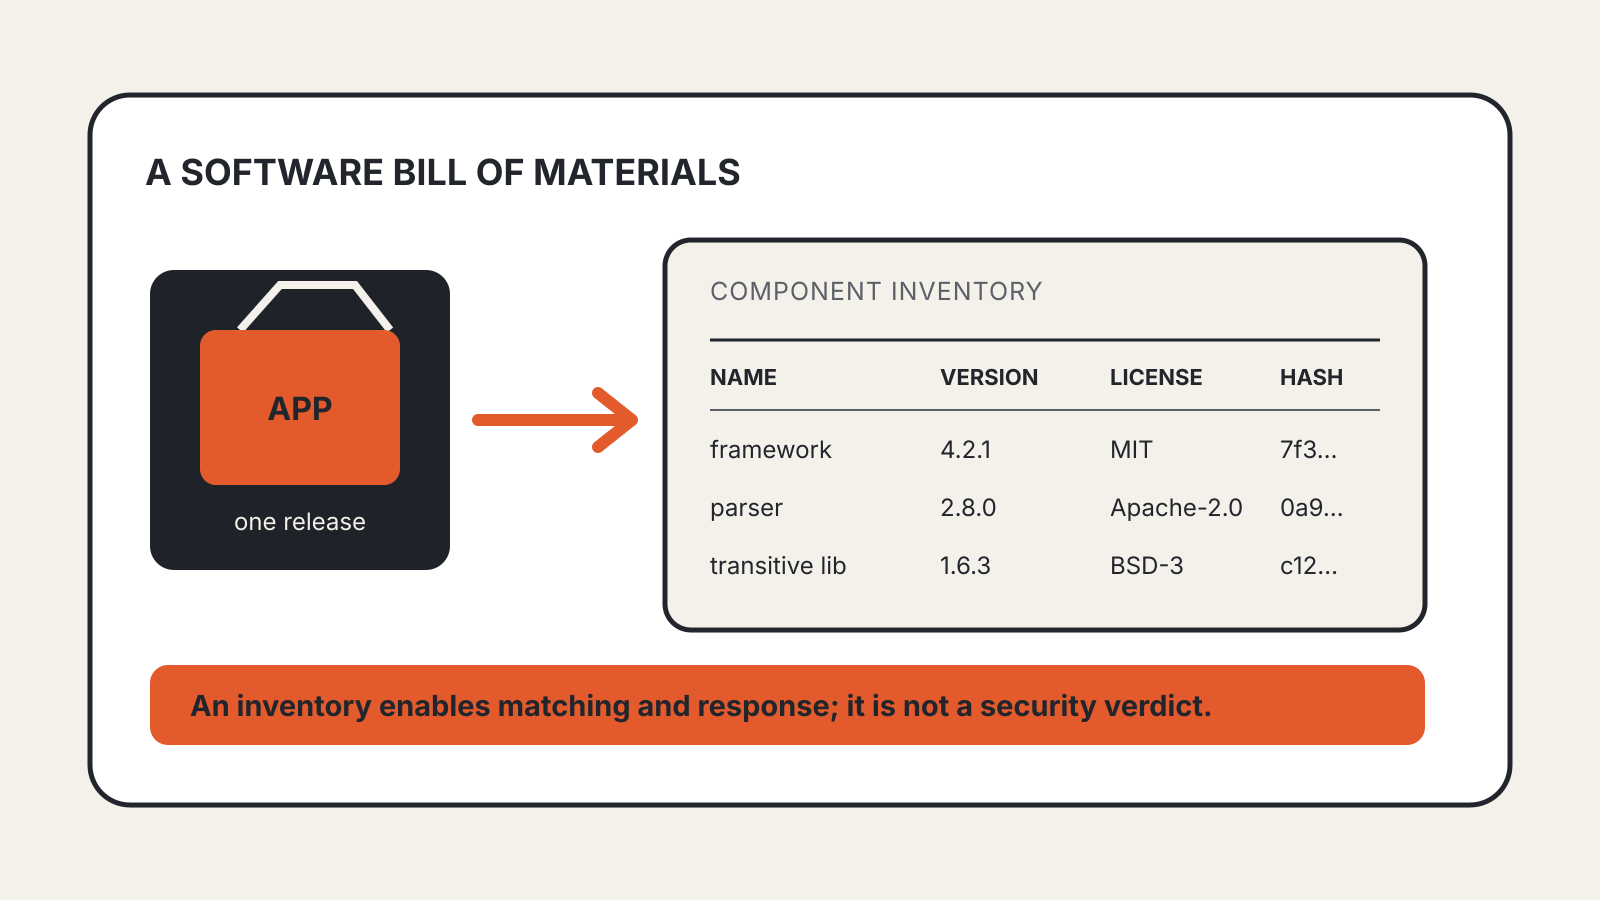
SBOM Explained: What a Software Bill of Materials Lists
What an SBOM records, how teams use it in vulnerability response, and why an inventory is not a security verdict.
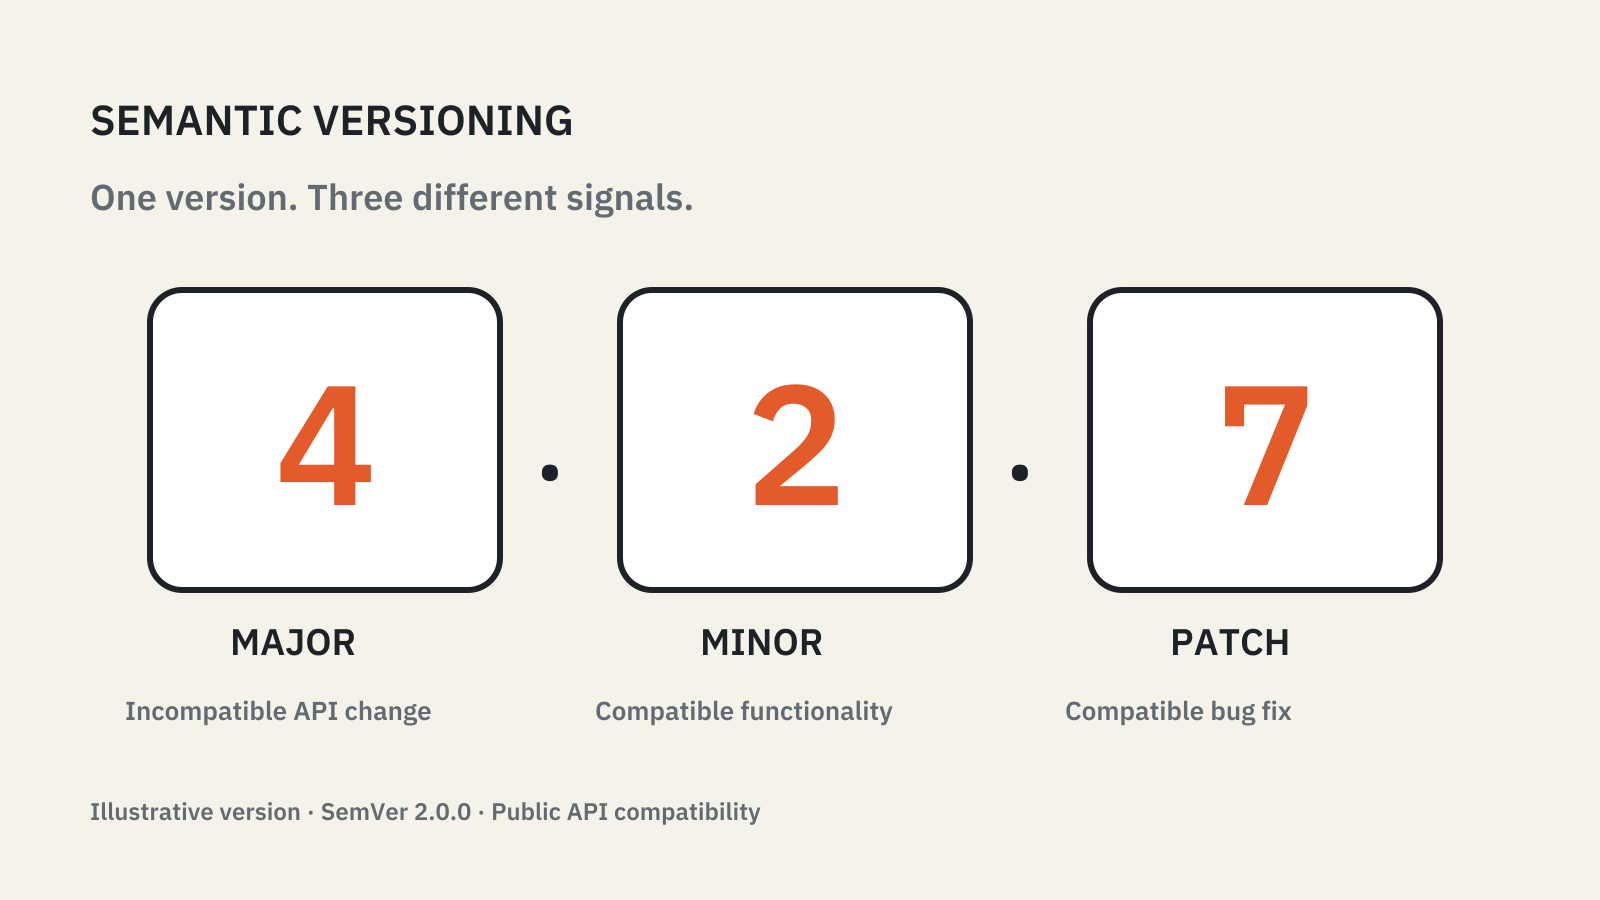
Semantic Versioning Explained: Major, Minor and Patch
Major, minor and patch describe API compatibility; your dependency range and lockfile decide what gets installed.